What to Do After a Ransomware Attack: The First 60 Minutes
September 25, 2026
The first hour after ransomware is for isolation, coordination, and evidence—not a scramble to restore everything. Here is what that hour can look like.
September 25, 2026
The first hour after ransomware is for isolation, coordination, and evidence—not a scramble to restore everything. Here is what that hour can look like.
September 23, 2026
A usable business continuity plan answers how essential functions keep operating when internet, payments, cloud apps, or IT systems fail—not just how technology gets restored.
September 21, 2026
Before asking what a new platform can do, businesses should define the problem they are trying to solve, the full cost of the investment, and what success will look like.
September 18, 2026
Employees often adopt unapproved apps, personal cloud storage, and AI tools to work faster. Shadow IT starts as a productivity shortcut, but it can become a cybersecurity, compliance, and access-management problem.
September 16, 2026
Many technology expenses are more predictable than they appear. With an inventory, lifecycle plan, and a 12-to-36-month roadmap, businesses can turn surprise IT costs into planned investments.
September 14, 2026
Employee offboarding is more than an HR checklist. If email, cloud apps, remote access, devices, and shared passwords are not removed, a former employee can leave while their digital access remains.

September 11, 2026
Most cybersecurity and compliance problems start small. The longer those gaps sit unaddressed, the more they can affect insurance, contracts, continuity, and the time required to correct them later.
September 9, 2026
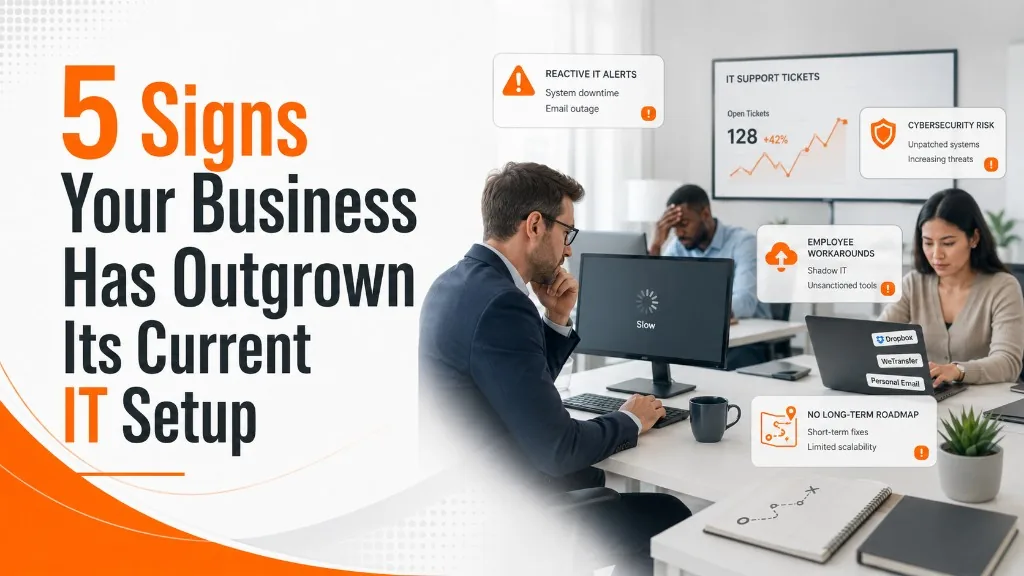
A business has generally outgrown its IT setup when technology begins creating recurring friction, risk, or unexpected costs instead of supporting day-to-day work and future growth. Here are five common signs to watch for.
September 8, 2026
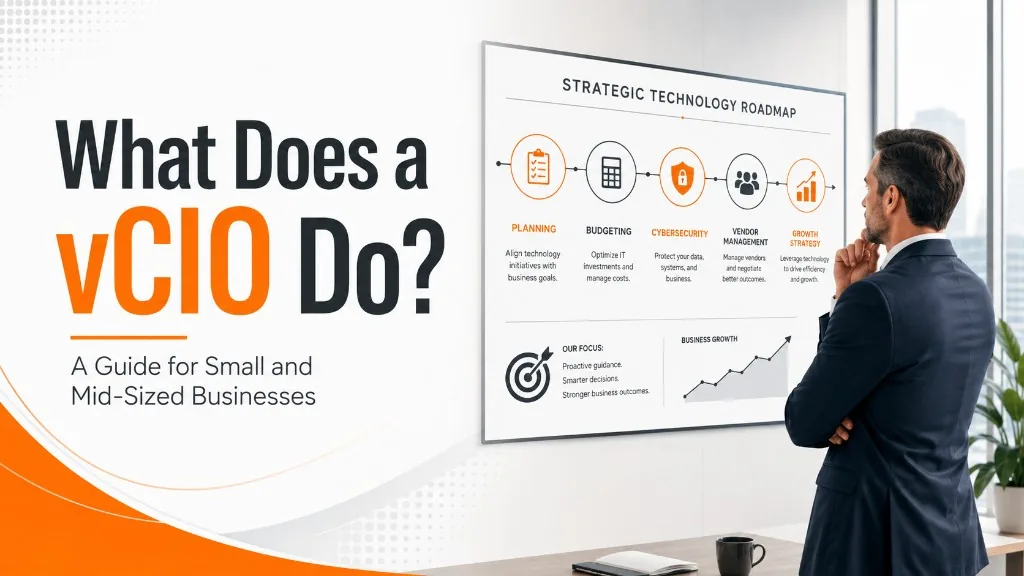
A vCIO is a technology advisor who helps a business make strategic decisions about its IT environment—building a roadmap, planning the budget, prioritizing cybersecurity, and aligning technology with business goals.
September 4, 2026
Being ready for a SOC 2 examination does not mean scrambling to create a stack of policies right before an auditor arrives. It means building repeatable security and operational processes that produce evidence as part of normal business operations.